Warnings from the FBI and CISA came in loud and clear…Scattered Spider’s cyberattacks are more hazardous and crippling than ever before. Their high-profile, financially motivated attacks rely on social engineering for data theft, extortion, and ransomware attacks. And when both security agencies release a joint advisory warning to us about this threat group, it’s smart to listen.
These threat actors made headlines for crippling financial attacks against MGM Resorts International, Caesar’s Entertainment, and Okta. Although they refused to pay the ransom demand, MGM’s attack alone cost the company more than $100 million in losses.
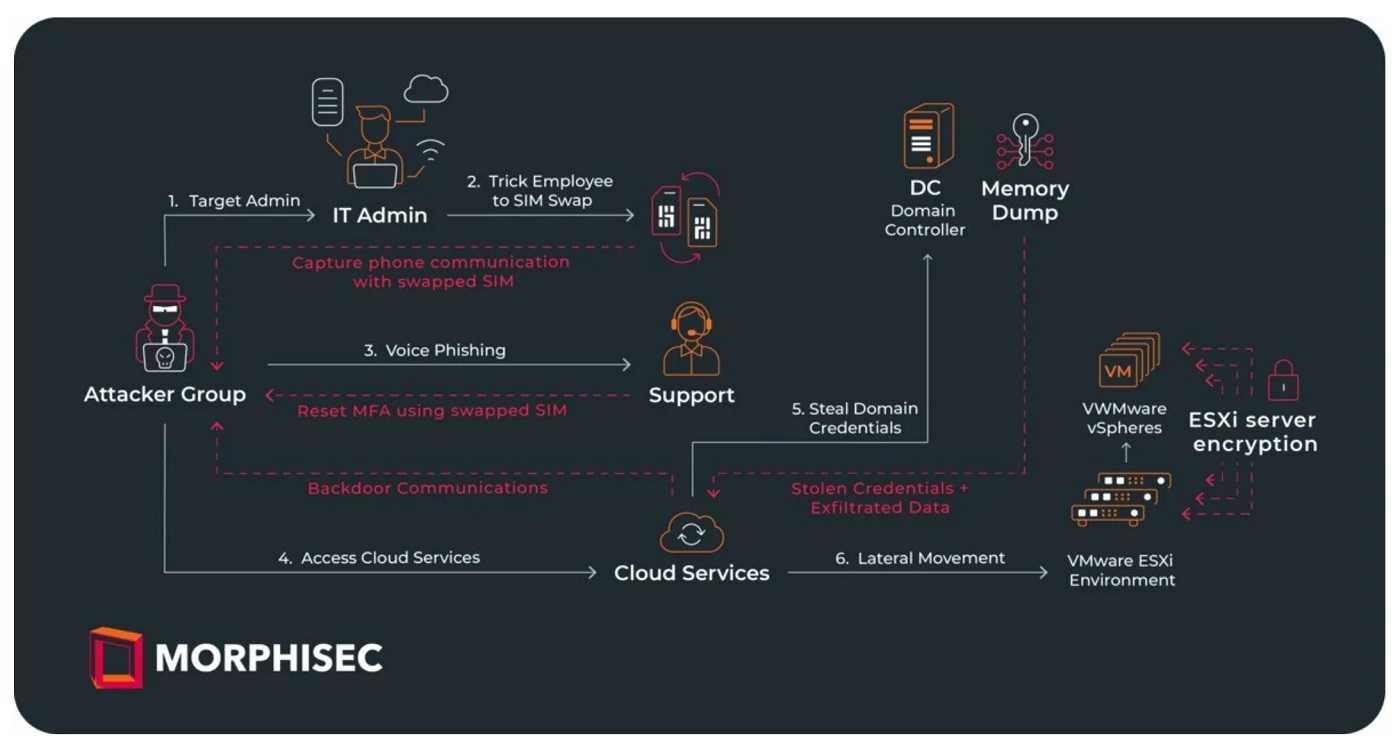
Scattered Spider gained entrance to MGM’s systems after finding an employee’s profile on LinkedIn, giving the group what they needed for their socially engineered phone call (vishing) attack. Just one phone call led to them stealing a trove of sensitive data and unleashing BlackCat ransomware on the entertainment behemoth.
2
Since 2022, Scattered Spider, aka Oktapus/Octo Tempest, began making headlines. The group didn’t waste time using an arsenal of weapons for financial crimes. They’re considered experts in social engineering and big money theft, as MGM and others lived to tell.
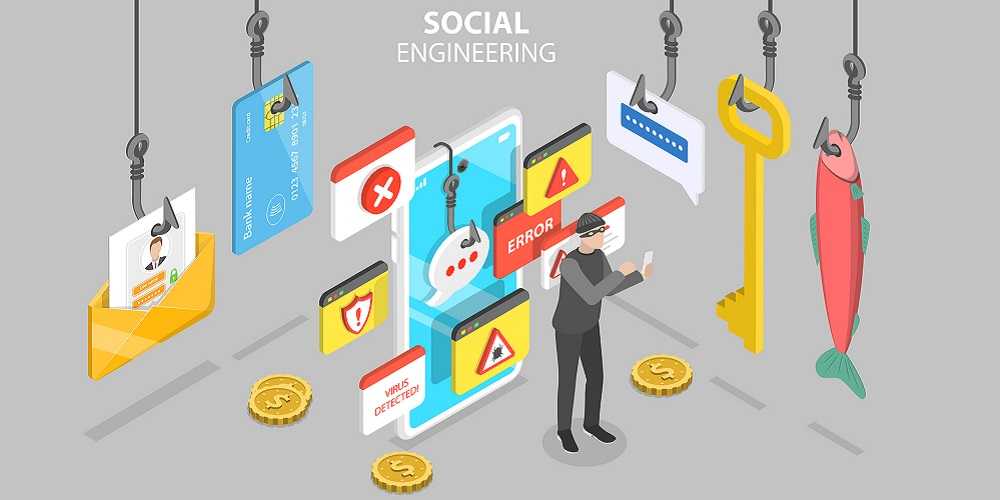
Scattered Spider’s socially engineered attacks trick potential victims with phishing techniques and expert deception. A staffer is convinced that the text, email, or phone caller is legitimate. They’re tricked into giving up information the group exploits, giving them a foothold for their eventual ransomware attack.
As the FBI/CISA advisory warns about Scattered Spider’s weapons and tactics "After identifying usernames, passwords, PII, and conducting SIM swaps, the threat actors then use social engineering techniques to convince IT help desk personnel to reset passwords and/or MFA tokens…” Their techniques also use account takeovers (ATO), push bombing, installing remote access tools, and others they have waiting in their web.
Only Scattered Spider knows who their next victim will be, but we can be sure they’re spinning a web ready to put them back in the headlines soon.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.