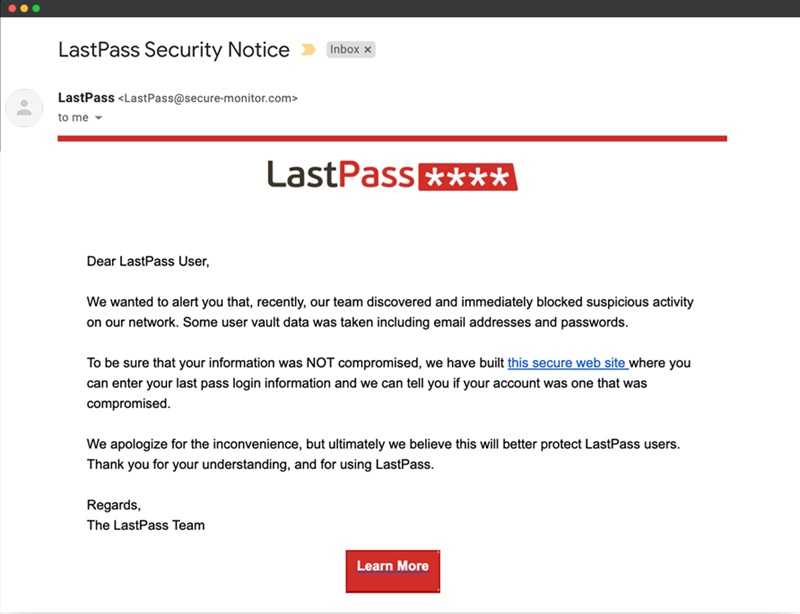
In what may be one of the more twisted phishing campaigns we’ve seen lately, users of the password manager LastPass are being told a “death certificate has been uploaded” in their name. But clearly, they are alive. So what gives? Well, the scam works like this: a user receives an email that claims someone has submitted their death certificate to LastPass’s “legacy access” feature, requesting access to the user’s vault. The email includes fabricated details including a case number, “agent ID,” and urgent deadline. All of this is designed to freak out the target into acting immediately.
If the user does fall for it, when he or she clicks the link, they are directed to a very convincing fake LastPass-login page (such as lastpassrecovery[.]com) that harvests the master password (and in some cases passkeys) once entered. Behind the scenes, the campaign is believed to be carried out by the threat group known as CryptoChameleon (aka UNC5356), which has a track record of targeting cryptocurrency wallets and password managers.
So, how can you avoid falling into the trap?
If you receive any email claiming you’re deceased or that someone uploaded a death certificate in your name, stay calm. Whatever you do, don’t click the link. Next, go directly to your LastPass account using a link you know is legitimate and check if anything is amiss. While you’re in there, ensure you have multifactor authentication (MFA) enabled. Remember, if there is an option available for MFA such as using a one-time code generator app or biometric ID, choose one of those over a text or email code.
Finally, change your master password in your LastPass account. Better to be safe than sorry. Just don’t follow the link in the email!
Never provide login details using a link provided in an email; especially if the information in the account are very personal and confidential. Always go directly to your account using links you trust, such as the ones you’ve bookmarked.
This attack has been ongoing and is expected to continue. According to some reports, the phishers are even calling victims on the phone, using social engineering techniques and getting the login details. Don’t fall for it.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.