Hackers Are Targeting AI to Infect the Apps You Trust
By: Jim Stickley and Tina Davis
September 29, 2026
Most people don't think twice before installing an app update. After all, updates are supposed to make software safer and more reliable. But security researchers are warning about a newer tactic that could turn trusted software into an unwitting delivery system for malware.
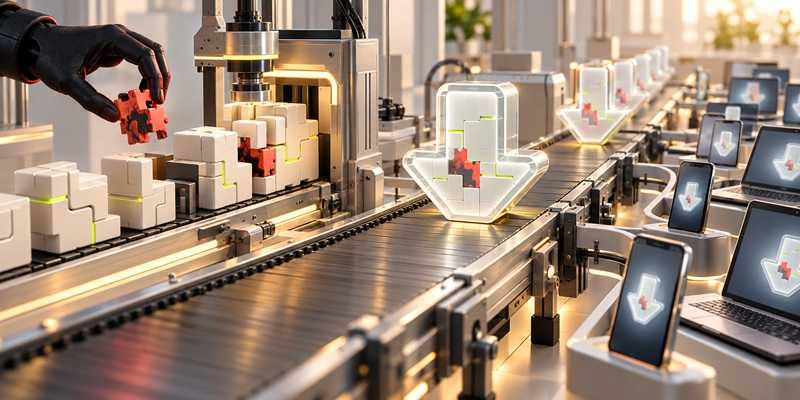
Instead of attacking consumers directly, cybercriminals are increasingly targeting the people who build software. Researchers say attackers are attempting to manipulate AI coding assistants, poison software packages used by developers, and insert malicious code into the software supply chain. If successful, that harmful code can eventually find its way into legitimate applications downloaded by thousands or even millions of users.
The strategy is both clever and concerning.
The average person isn't likely to encounter one of these attacks directly, but they could experience the consequences. If malicious code slips into a trusted application, users may unknowingly install malware simply by downloading what appears to be a legitimate software update.
Modern developers often rely on AI-powered coding assistants to speed up programming tasks and use open-source software packages to avoid reinventing the wheel. Criminals are exploiting that trust by creating fake software libraries, modifying legitimate code, or attempting to trick AI tools into recommending malicious packages. A developer may unknowingly include one of these compromised components in an application, allowing malware to spread far beyond the original target.
The good news is that software companies and cybersecurity researchers are becoming increasingly aware of these tactics. Many organizations now scan software for suspicious components, verify the origin of third-party code, and require additional security reviews before releasing updates.
For consumers, the best defense remains surprisingly simple. Download software only from official app stores or trusted company websites. In other words, don’t side load applications. You’re just asking for trouble. Install updates for apps promptly and remove applications you no longer use. These habits reduce your chances of installing compromised software if a supply chain attack occurs.
Cybercriminals are always looking for the path of least resistance. Today, that path may not be through your device at all. It may start with the software developer creating the apps you trust. That's why protecting the software supply chain has become one of cybersecurity's fastest-growing priorities.
 SUBSCRIBE TO WEEKLY NEWSLETTER