

It’s remarkable and scary. Data breaches are experiencing a huge jump in public reporting. These breaches are disturbing enough on their own. However, they are also providing opportunities for an increase in other cybercrimes. According to the 2015 Internet Organized Crime Threat Assessment (IOCTA), the increase in data breaches is leading to a variety of secondary crimes such as fraud, extortion, and similar crimes which are increasing substantially. It’s a cybercrime trend happening the world over.
Comparing their results to 2013, it’s a 49% increase in breaches, and a whopping 78% rise in stolen or lost data records. According to the BLI, breaches of identity theft took up one-third of the category they call “catastrophic” or “severe.”over 1,500 data breaches in 2014 led to one billion compromised data records worldwideThe Breach Level Inedex (BLI), a database that collects data for global breaches, released its results for 2014. Backing-up what the IOCTA reports, 
Reporting data breaches has become the law in most states in the U.S. According to the National Conference of State Legislatures (NCSL), legislation exists that requires “private or government entities to notify individuals of security breaches of information involving personally identifiable information.” NCSL reports as of June, 2015, the only states lacking data breach legislation are Alabama, New Mexico, and South Dakota.
The response from the targeted businesses of data breaches is predictable, albeit very often too late. It’s more critical than ever for businesses to start thinking more proactively about their cyber security. Beefing up cybersecurity with higher levels of encryption and ongoing employee education are prerequisite for avoiding repeat thefts.
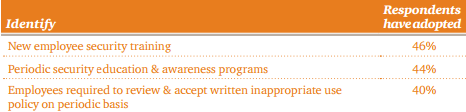
According to the 2014 U.S. State of Cybercrime report, 42% of those responding to surveys said that security awareness programs and training on security for new employees played a role in deterring potential crimes. This was the most successful of all the policies employed for cybercrime prevention. In addition, those organizations that did not train new hires on security reported $521,000 more in annual financial losses than those who did.
In addition to education, here are ways to lower the risk of a data breach:
- Implementing multi-factor authentication for all persons who access business networks via remote connections or online applications. This could be a fob technology or a text message with a unique code that needs to be entered before access is granted.
- If you choose to allow personal devices to connect to your corporate network, consider a strict policy and enforce it. This should include requirements for all users to have strong passwords and install anti-malware and keep it updated on all devices.
- Create and implement an employee and contractor access exit strategy. This means that as soon as a resource leaves or no longer needs access to your environment, that access is immediately cut off. This should include changing all administrator passwords if the exiting resource had access to them at any time.
- No matter the size of your organization, everyone with access to your network should be required to sign a confidentiality agreement that includes verbiage that passwords will never be shared with anyone. That includes giving them to the IT staff.
- Create, review, and update an incident response plan. It should include details on who is on the team, how to reach them at any time, if needed, and who is responsible for what tasks. No matter how thorough the plan is, it will not be effective if it isn’t kept up to date. Review it at least annually and practice it too.
This is by no means an exhaustive list and each organization needs to determine the strategy that works best for it.
According to survey results from SafeNet, a US based data protection company. 65% less likely to continue doing business with these companiesUnfortunately, because of the rise in data breaches and the reporting of them, the damage done to individuals with stolen information is creating a very negative response. Consumers affected by large scale data breaches such as Target, AOL, and eBay are
The tendrils of security breaches are reaching higher and further than anyone may have expected. The end result potentially touching each of us in ways over which we have no control. The fear of this lack of control over one’s very private information is a disturbing concept. Many experts feel the future of data breaches will in one way or another affect us all.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




