

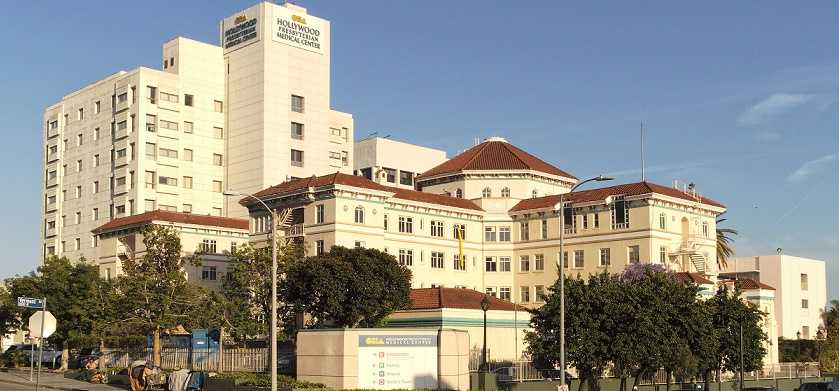
Recently the Hollywood Presbyterian Medical Center paid $17,000 in Bitcoin currency to hackers. You may be asking, “Why?” It comes down to life and death. The hackers were able to get ransomware executed on the hospital computer systems which kept them locked up for over a week. It simply was in the best interest of the organization and the patients for them to do it. However, was it the right choice?
 Some may say so, but there is a much better way to deal with this situation. A comprehensive multi-level security program is the key. It should include technology such as firewalls and intrusion prevention systems, but also include a plan for backing up important files and systems, a training and education program on cyber threats and prevention, and an incident response plan (IRP) at a bare minimum.
First and foremost, all organizations should have their systems backed up regularly. In the case of a hospital where life and death truly is at stake, that cycle should be very frequent; no less than nightly.
In addition, educating employees, staff, doctors, and all other personnel that are using the organization’s system, on phishing and how to avoid becoming a victim is of the utmost importance. Yes, it is expensive to hire someone to do training and cyber security education. However, there are companies out there that will provide such services for less than someone’s annual salary and in some cases, much less. If you are in charge of a network, this is money well spent. In fact phishing is the number one way malware gets executed on networks.
Finally, an IRP that is well thought out, practiced, reviewed, and updated could save an organization a lot of pain and suffering. True, that at the point you have to execute the plan, something has happened. However, being able to quickly react to a situation could prevent a bad, but manageable situation from becoming a complete financial, political, and reputational nightmare.
 Many medical devices are connected to the hospital or medical center’s network. This means that anyone on the same network who executes malware on their computer, also affects all of those devices. So, if someone in administration falls victim to a phishing attack and causes ransomware to execute, it could affect patient monitoring systems or insulin pumps. This could make it truly life or death. This is how the Hollywood Presbyterian Medical Center got in this situation.
Hospitals and medical facilities are estimated to be roughly 10-15 years behind the financial industry in implementing cyber threat prevention measures and in educating employees and staff on the topic. As a result, they are easy targets for hackers who want to extort massive amounts of money or who want to sell all the data they can retrieve from medical records on the black market. In fact, security company Trustwave has said that it costs about $5,900 to create ransomware using DIY kits. That may result in revenue of $90,000 for the perpetrators with very low risk of ever being caught. If they actually get access to patient records, it could ultimately be more. That’s a pretty good day at the office for most.
Paying the money to get a key to decrypt files may be recommended by the FBI, but it isn’t recommended by most security experts. A much better way to handle the situation is to restore files from backups and then execute the IRP. Patients will be safe and the hackers will not be rewarded.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




