

The FBI recently released a warning to those in the healthcare industry about attacks on FTP servers running in “anonymous” mode. The agency said that cybercriminals are targeting the servers in order to “access protected health information and personally identifiable information in order to intimidate, harass and blackmail business owners.”
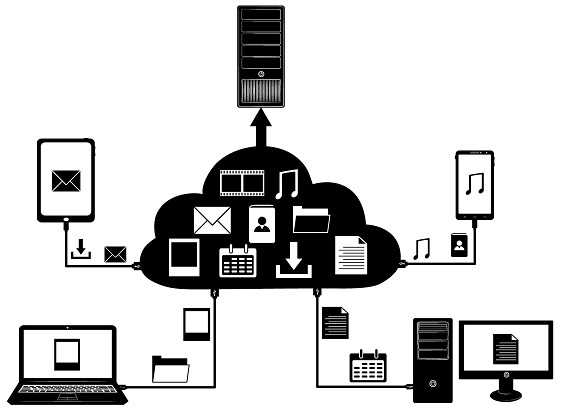 There are some recommendations for those who do use this service. And even if it is secured, those with which an organization does business and exchanges information may not. Make sure that those third parties do not allow the use of FTP in anonymous mode.
In addition:
- Apply security and critical patches to the FTP server as soon as possible.
- Only give access to the FTP server to those who really need it.
- Ensure that the servers are not using default settings.
- Review event logs regularly and use real-time monitoring to have suspicious and abnormal alerts sent to someone who can address them right away.
- If it is necessary to store data on FTP servers, make sure it is encrypted.
- Block incoming traffic from untrusted sites.
- Keep updated antivirus and antimalware on the FTP servers.
- Use a dedicated FTP server that is not used for other purposes, particularly for storing sensitive data.
 Ransomware has spiked in the healthcare industry in the past year. Because of the type of and amount of data that the healthcare industry has stored on people, it is particularly vulnerable to attacks. Hackers will access it and subsequently threaten to post the stolen information publicly, sell it on the Dark Web, or wipe out patient and other data unless ransom is paid. Since last summer, a hacker that is known as TheDarkOverlord has been harassing some in the healthcare sector and threatening them with extortion.
However, rather than pay off these thieves, ensure that regular backups are done regularly on any sensitive or patient data. If this is part of normal operating procedures, then the need to pay the hackers to retrieve the data will not strike as it did for Hollywood Presbyterian Medical Center. It paid the hackers to decrypt the data, as they did not have current backups in place with which to restore it.
It isn’t just the healthcare industry that is vulnerable to this FTP attack. Others must also secure these servers. Merely encrypting the data during transmission is not sufficient.
The FBI statement included that “In general, any misconfigured or unsecured server operating on a business network on which sensitive information is stored or processed exposes the business to data theft and compromise by cybercriminals who can use the data for criminal purposes such as blackmail, identity theft or financial fraud.”
Anonymous FTP (file transfer protocol) mode means that logins to the service do not require a named account. Therefore, just about anyone who knows anything about this type of service can get onto the server.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




