

In 2015 organizations spent $75 billion on cyber security products. That number is projected to increase to over $100 billion by 2020. That’s an incredible amount of money being spent by organizations all over the world to reduce their risk to cyber attacks. Yet, even with this huge expenditure it’s hard to go a day without reading about another organization that has fallen victim to malware, a breach, and/or cyber extortion. What makes this so confusing is that security technology is the best it has ever been and clearly, organizations are spending the money in an effort to prevent the success of these attacks. So how come it seems things are getting worse rather than better? The answer is surprisingly simple; it’s you.
To be fair, it’s possible that it may not specifically be you. However, statistically speaking one out of every 10 employees is a major security risk to his or her organization. This means there is a one in 10 chance that you personally could put your organization at risk.
 It wasn’t so long ago that when you read about an organization experiencing a cyber security breach, the details would reveal that the hacker started the attack by exploiting an Internet service such as a mail or web server on an organization’s network. These exploits were often discovered on improperly patched or poorly secured servers that cybercriminals would find through basic network scanning. Once on these compromised servers, the hackers would use them as a conduit into others on the network gaining more and more access until they got to the confidential and/or private information.
However, times have changed and the ease at targeting these Internet based servers has all but dried up. Why is this?
First, many organizations have now turned to cloud based solutions to host services they once ran on their own networks. This means that even if hackers gain control of one of these servers, they still don’t have a connection to the corporate network itself. In addition, cloud based solutions have proven to be far more secure since the organizations hosting them dedicate the time required to properly patch and maintain the software. This eliminates the easy points of attack.
Second, organizations that do opt to run their own services have also stepped up their games. Gone are the days when you find an unpatched server directly accessible via the Internet. And with the latest in firewall and intrusion prevention solutions implemented, exploiting Internet facing equipment is real work.
 So, with technology reducing the success a cybercriminal might have attacking networks via the Internet, a change in tactics was needed. It turned out that the solution was to go after you, the employee. Ultimately cybercriminals are looking for access; access to servers, access to software and access to personal and confidential information. It turns out that employees generally already have this, which means that if a cyber criminal can exploit the employee, they will have the same access as that employee.
With this realization, cybercriminals began shifting their attacks towards employees and ever since, you have seen their daily onslaught of breached corporations all over the world.
So how do they do it? The most successful form of attack is via email. By now everyone has heard of the term spear-phishing and understands that criminals will send emails that look like they come from legitimate sources. What is surprising though, is that up to 40% of an organization’s workforce will still fall victim to these types of attacks. How is that possible? Most people think they can spot a phishing email just by looking at it. The reality is that cybercriminals have become very skilled at creating emails that look real. Often they will contain the recipient’s first and last name, personal information, and details that the recipient believes only the sender would know.
Criminals also focus on malicious website attacks. When an organization falls victim to a cyber attack, the first thought is that it must have been specifically targeted. But chances are that the cybercriminal was not even aware of the organization until after it was breached. You see, criminals will often set up “traps” on the Internet with the hope that unsuspecting individuals will happen upon them and get sucked in. Your computer has vulnerabilities from time to time. Often, these vulnerabilities are specifically related to your web browser and applications that run via your web browser. While keeping up with patches can reduce the risk these vulnerabilities create, there are still times when a patch is simply not available. To take advantage of these weaknesses, cybercriminals will create websites designed to lure people in.
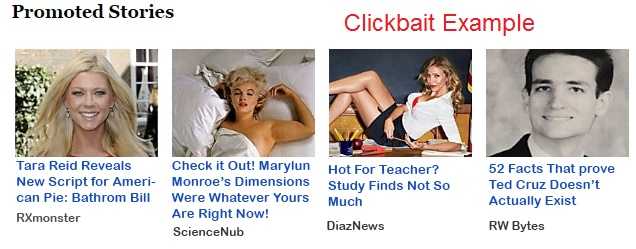 Often they will drive victims to their sites through Google ads or other advertising options. If you happen to be browsing on the Internet and end up at a criminal’s website, everything will seem normal. In most cases whatever information was advertised to be available on the site will be there. Often this will be cyber security information, news about breaking stories, or gossip about popular celebrities. The content is irrelevant and simply provided as a way to entice users to visit. What is important is the underlying code running on the server, designed to exploit vulnerable web browsers and install malware. Adobe Flash, a popular third party application that is loaded on most Windows based PC’s is often the target of these types of attacks. Keep in mind that while on the website, there will be no obvious indication that malware is being installed and the entire process takes less than a few seconds.
While obviously there are many ways in which employees are targeted by cybercriminals, the goal is always the same; to gain access to the victim's computer and ultimately to the corporate network. This is why it is so important that you understand the risk you personally pose to the corporate network. Every communication you have via email, every conversation you have over the phone, and every website you browse on the Internet are all potential access points for would-be cybercriminals. And while security technology continues to advance, the reality is that human mistakes not only negate the effectiveness of that technology, but often times those mistakes also render the security solutions completely irrelevant.
The best tip you can remember is that before you click a link, open an attachment, or share information over the phone, stop. Take a moment to think about the action you are about to preform and when in doubt, pick up the phone and confirm with someone in your organization that what you’re about to do is safe.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




