

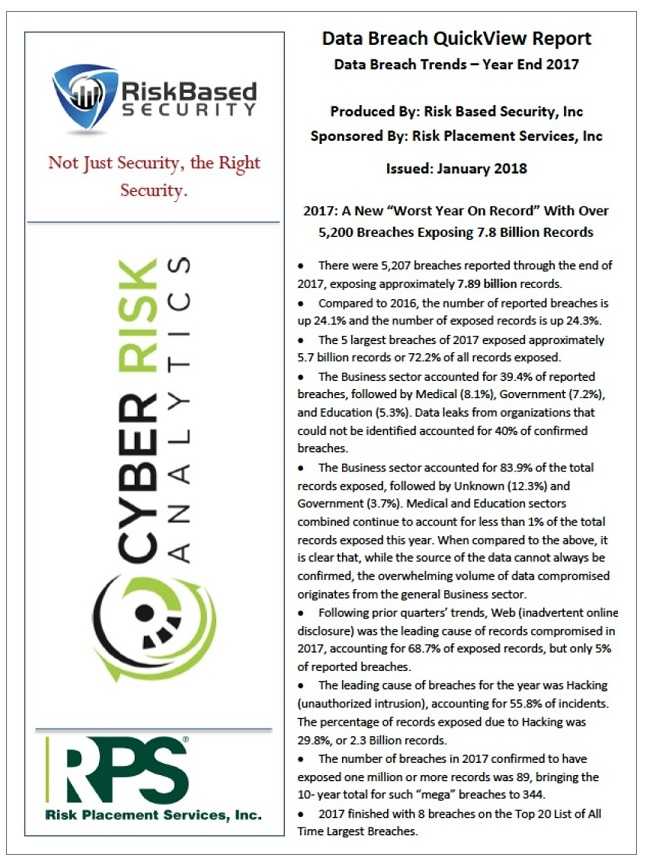
Last year was a big year for data breaches. Not only were intrusions (hacking) big news, so were accidental exposures and mistakes. Believe it or not, last year there were 5,207 breaches. These resulted in theft of 7.89 billion information records. Both stats are according to Risk Based Security, which put together these numbers from public disclosure data.
 Hacking has historically been the top method for data breaches, and it remained on top for 2017. However, those incidents did not result in the most exposed records. That number was due to unintentional exposure. This could have been because of misconfigured services and devices, loss or theft, or accidents and human errors. Approximately 5.4 billion (68.7%) records were exposed this way, while 2.3 billion were due to hacking.
There were several instances of misconfigured Amazon Web Services (AWS) servers in 2017. According to RedLock CSI, 53% of businesses using such cloud services had accidently exposed at least one of their cloud services. Among the big ones in this category were Accenture, Booz Allen Hamilton, and Verizon.
Eight of the largest reported data breaches found themselves in the top 20 list of all time largest; the five biggest resulted in exposure of 72.2% of the records. Contributing were the massive breach of Equifax (145.5 million records) and Sabre Systems in August of 2017, which has not reported the full extent of the breach. However, it affected at least 14 hotels in the Trump Hotel Collection and Risk Based Security reports that it is still getting information on additional data exposure from organizations like travel companies and hotels that used Sabre’s services.
 The U.S. led the rest of the world with most reported breaches, by a long shot with 2,330. The next closest was the UK with 184, then Canada at 116. However, the significant difference is likely due to reporting requirements already in place in the U.S. In May of this year, the European Union will implement the General Data Protection Regulation (GDPR), which includes breach notification rules. At that time, it’s expected that the numbers in that region will also increase.
Even with the largest number of reported breaches, the U.S. still had fewer records lost in the incidents. The prize for that went to China with 11.8 million, followed by South Africa at 6.7 million.
The business sector had the highest amount of exposed records (82.9%), with government, medical/healthcare, and education a very distance second (3.7%), third (less than 1%), and forth (also less than 1%), respectively.
Advice to all organizations is to continue and step up security awareness training. A comprehensive program should include training staff, consultants, and even third parties on the latest risks, threats, and mitigation as well as information on what makes them targets and what type of information the attackers want from them. This will help them avoid making your business part of these figures.
 And just because we know you’re on the edge of the seat to know, the top five data breaches of all time (with regard to breached records) were:
- Yahoo (U.S.) – 3 billion
- DU Caller Group (China) – 2 billion
- River City Media (U.S.) – 1.3 billion
- NetEase (China) – 1.2 billion
- Undisclosed organization (Netherlands) – 711 million
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




