

Business Email Compromise (BEC) scams are not new. In fact, the FBI’s Internet Crime Complaint Center (IC3) is reporting that there has been a 2,370 percent increase in these types of cybercrimes; both attempted and successes. An active one, according to IBM’s X-Force Unit is currently targeting Fortune 500 companies. It isn’t limited to a particular industry, as there have been victims in retail, professional services, healthcare, and the financial sectors.
While there are numerous ways to perpetrate BEC attacks, in the case of the current scam, users on accounts payable teams are being targeted. Social engineering and phishing email are being used. Particularly, a “phishing kit,” that spoofs the digital signature DocuSign login pages is the bait that tricks people out of their network and email login credentials. The messages appear to be from legitimate contacts from the employee’s address book.
This one uses the particularly bothersome method of infiltrating email chain conversations and active discussions to find out more about current payments and projects. By doing this, the likelihood of someone clicking on a link or attachment is significantly increased.
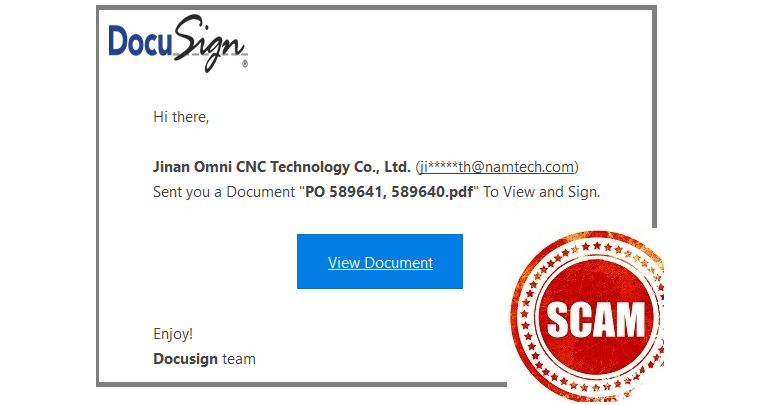
As many times as it's repeated and as many people know about phishing, it's still shocking that so many people still get hooked on phishing lures. If you are not expecting a link or attachment, don’t open it. And even if you are, second-guess it before clicking. Make sure you verify with the sender that it was indeed their intention to send it at that moment. It’s getting more difficult to be confident about these messages anymore, so it really is going to take extra effort to make sure we don’t set malware loose on the corporate network. It’s certainly better to be the one that prevented a cyberattack than the one that gets blamed.
 It is not the first time DocuSign has been used in an attack. In both 2016 and 2017, DocuSign was in the cybersecurity news. Earlier this year another attack called FreeMilk made its way around the globe. It also used previous email conversations to distribute malware in phishing campaigns. This one, however does not use malware. Instead, it uses legitimate employee information and credentials to do its deeds. Therefore, traditional security products are ineffective in detecting it.
Trend Micro is predicting that BEC attacks are likely to exceed $9 billion in losses in 2018.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




