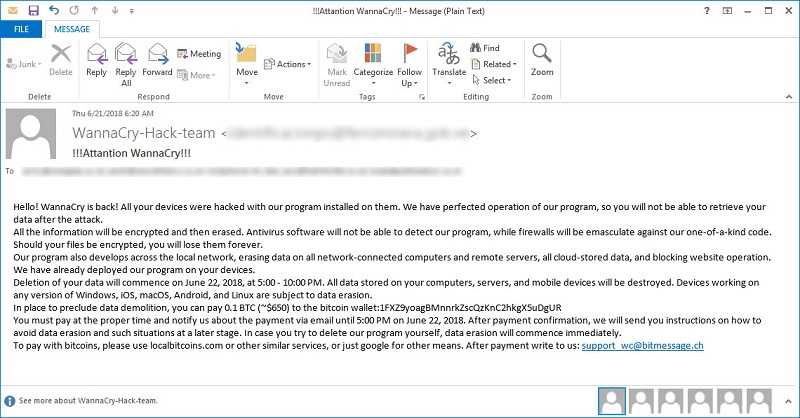
Sometimes it’s easier to just re-use someone else’s art, or in this case scam, than it is to be creative all on one’s own. And there is a group, calling itself WannaCry-Hack-Team trying to capitalize on the notoriety of the WannaCry ransomware that went around last year. The new scam has been seen on Reddit and was reported by a security expert at BleepingComputer. Essentially, users receive an email message claiming they have ransomware on their device and that they need to send bitcoin to get access back. But….there is a trick.
The users don’t actually have the ransomware. So, this scam is being termed WannaSpam, because that’s what it is. Some have called it WannaCrypt, because the files are not actually encrypted. The scammers just want the end users to think they are.
There are various subjects such as “!!!Attantion WannaCry!!!,” “Attantion WannCry,” “WannaCry-Team Attantion!!!,” and others. The great news about this is that if all of the subjects are as poorly written as these, it should be easy to identify as spam and a scam.
The good news is that you merely have to ignore this message. Nothing else is needed. Just ignore it….and delete it without any further action.
The spammers request .1 bitcoin for the ransom, which is roughly $628. They also claim that if isn’t sent within 24 hours, all data will be deleted. No worries though. They just WannaScam you.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.