

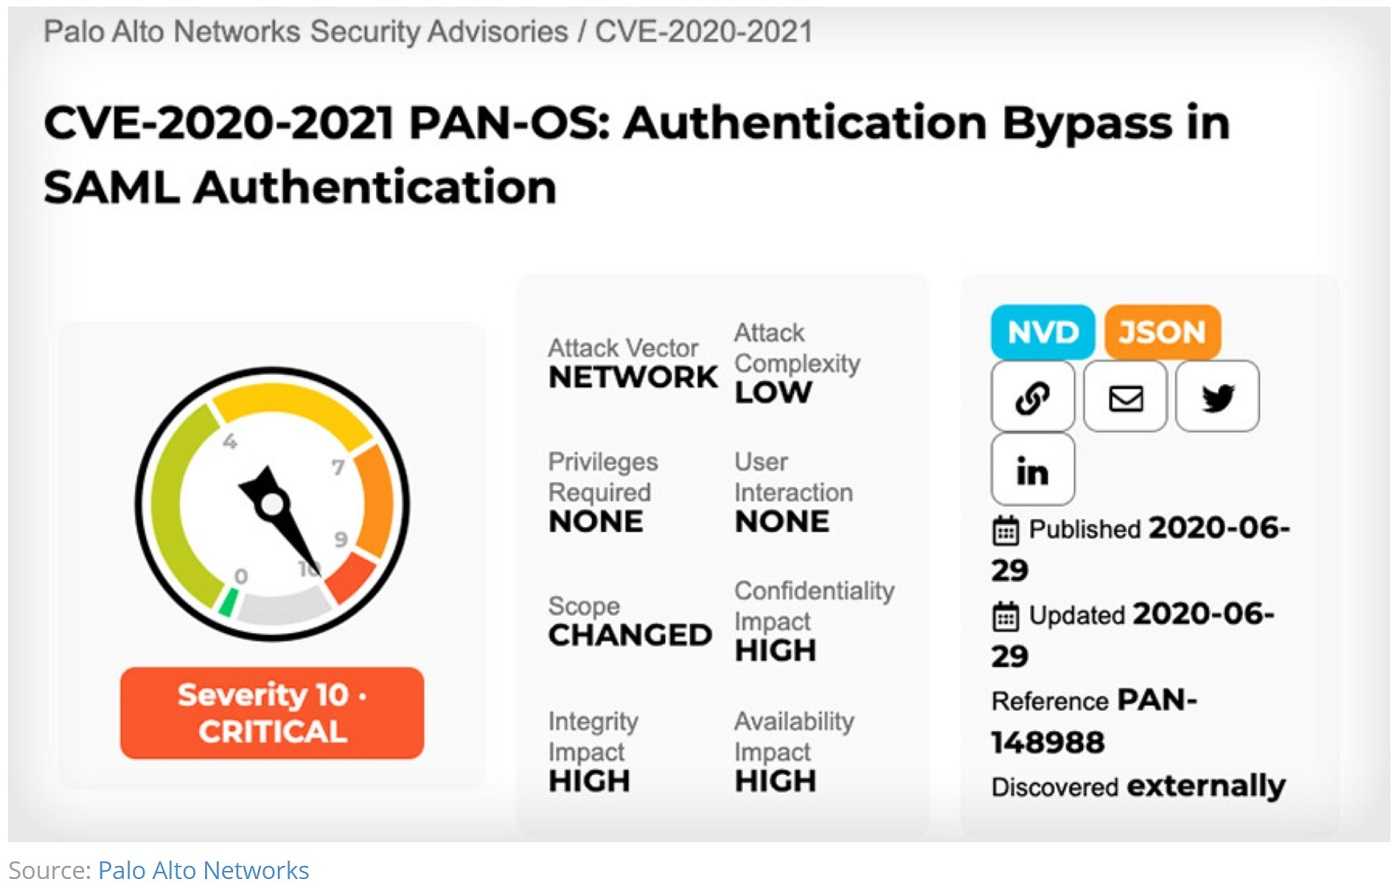
Most of us likely don’t know the brand of firewall or Virtual Private Network (VPN) used in our workplaces, and we usually don’t have to. Well, some people do need to know that information and ensure those products are doing their jobs and keeping their networks as secure as possible. Those people are typically working in your IT department. This week, it’s especially important for them to know if the firewall and/or VPN in their care are from Palo Alto Networks. That company along with the U.S. Cyber Command are warning customers to patch their PAN-OS systems immediately due to a serious flaw that is danger of exploitation by foreign state-sponsored hacking groups.
The flaw is numbered CVE-2020-2021 and a patch is available. If you use Palo Alto Network’s firewall, be sure to download the fix from the Palo Alto site and apply it right away. According to U.S. Cyber Command, foreign advanced persistent threat (APT) actors are likely to attempt exploiting it soon.
This bug is deemed Severity 10 - Critical, is easy to exploit and does not require any fancy technical skills to pull off. It can also be remotely executed and may bypass authentication. It’s a triple whammy of a vulnerability.
If it is exploited, hackers can change the operating system settings and potentially disable the firewall or VPN access-control policies. This essentially leaves the network completely open and unprotected.
Palo Alto Networks published a security advisory stating that if the “Validate Identity Provider Certificate” is disabled and the SAML (Security Assertion Markup Language) is enabled, is when the PAN-OS is vulnerable. These are not set up this way by default, so those administering these products should be sure to check the settings too. Devices that support both of those options include:
- GlobalProtect Gateway
- GlobalProtect Clientless VPN
- GlobalProtect Portal
- Prisma Access systems
- PAN-OS next gen firewalls and Panorama web interfaces
- Authentication and Captive Portal
Even if your products are not are vulnerable at the moment, it’s still important to ensure all patches and updates are applied as soon as they are released to avoid future bugs catching you off guard.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




