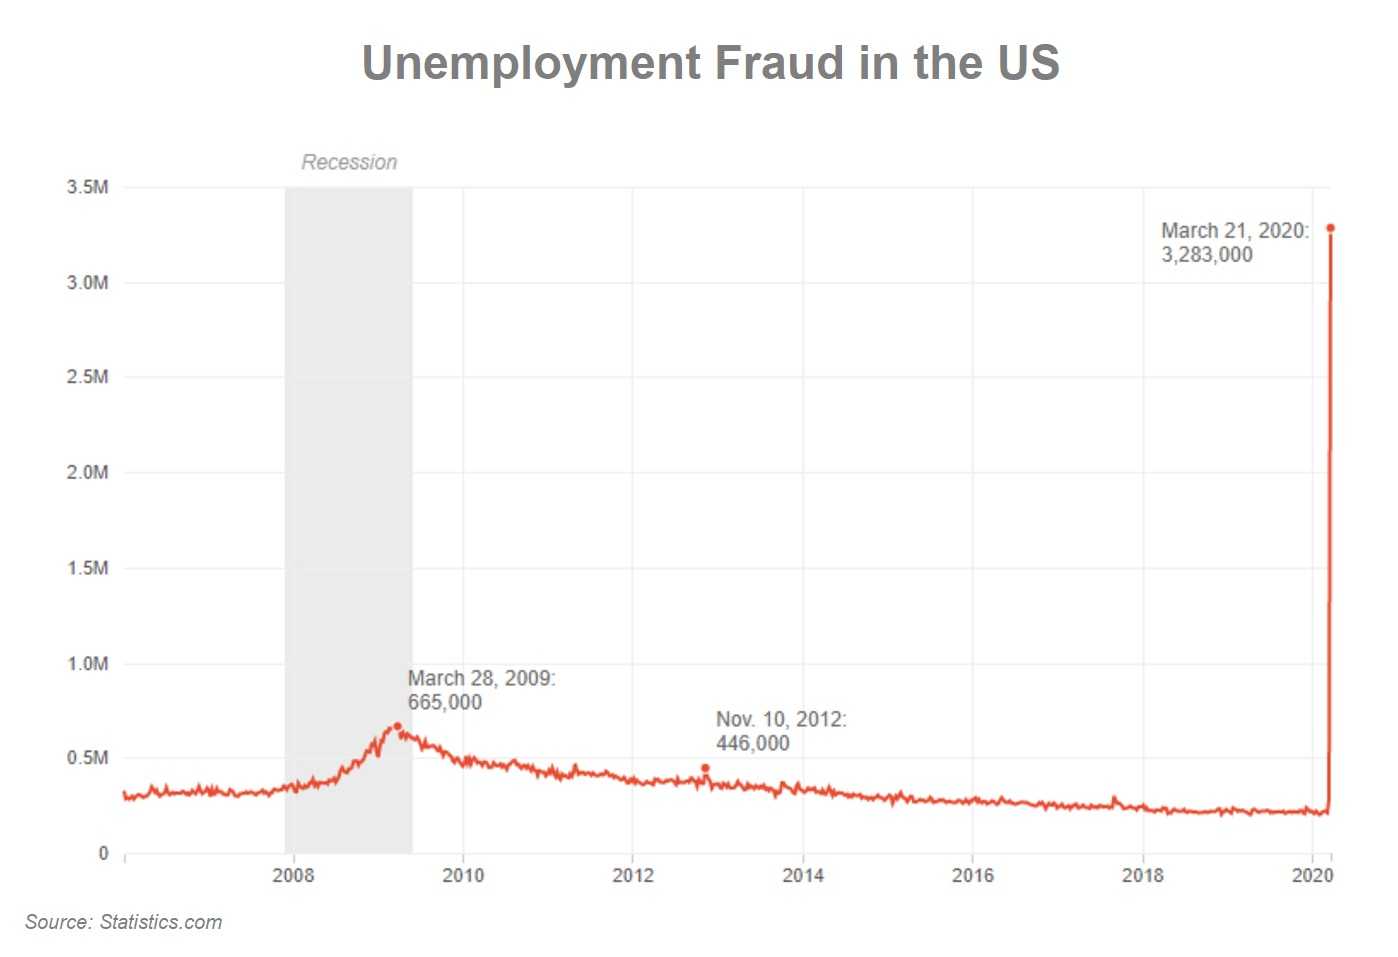
Since the pandemic started, using the coronavirus for internet and other scams has been a fruitful endeavor for hackers. Always looking for every bit of data they can steal, they’ve hijacked money, identities, financial information, and more using the coronavirus as a lure. They’ve successfully posed as FBI and IRS agents and Social Security representatives for months now. They’ve used fake virus cures, taken payments for PPE and other supplies that never arrived, filed fraudulent unemployment claims using stolen identities, and otherwise did their level best to scam citizens out of their first round of pandemic relief checks. Let’s make sure we don’t become victims this second time around.
2
The second wave of relief from the American Rescue Act is firmly in hacker crosshairs. Bad actors are using email phishing scams to install the Dridex banking trojan on trusting users’ devices. Researchers from Cofense discovered the phishing campaign started when citizens first learned the $1,400 pandemic relief checks would be forthcoming. It wasn’t by coincidence that hackers went into high gear at the same time, sending phishing emails that spoofed the IRS. The emails offer a bogus application for the financial benefits, but in reality, all the recipients received was the highly effective Dridex financial malware.
2
According to Cofense, there were typical warnings the emails were phishing scams. The email text includes nonsensical statements like “It is possible to get aid from the federal government of your choice,” offers a $4,000 check instead of $1,400, the ability to skip vaccination lines and other bizarre and non-existent help. An email button says, “Get apply form” and once clicked, they’re taken to a Dropbox account. The account holds an Excel document reading, “Fill this form below to accept Federal State Aid.” To see the entire form, victims are told to “enable content.” Once done, the Dridex infection chain begins, including its ability to avoid recognition by security software.
2
- The IRS never makes contact through emails and neither does the FBI. Snail mail is the way most government agencies do business, including never initiating phone calls. Social Security does send email blasts about general information, but the email never includes or requests personal data.
- Emails with bad grammar and spelling and those that require immediate action or sound too good to be true are all signs of a phishing scam.
- Verify the email sender and check the official website for the “government agency” sender. You’ll find the official website will tell you if the email content is truthful.
- Don’t use any contact information provided in the email or follow links or open attachments. You’ll likely be contacting the hacker’s call center setup, be led to a bogus web page that steals your personal data, or be opening a malicious attachment leading to the Dridex infection.
- If you suspect an email is phishing, remember “when in doubt, throw it out.” Chances are, you’ll be glad you did.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.