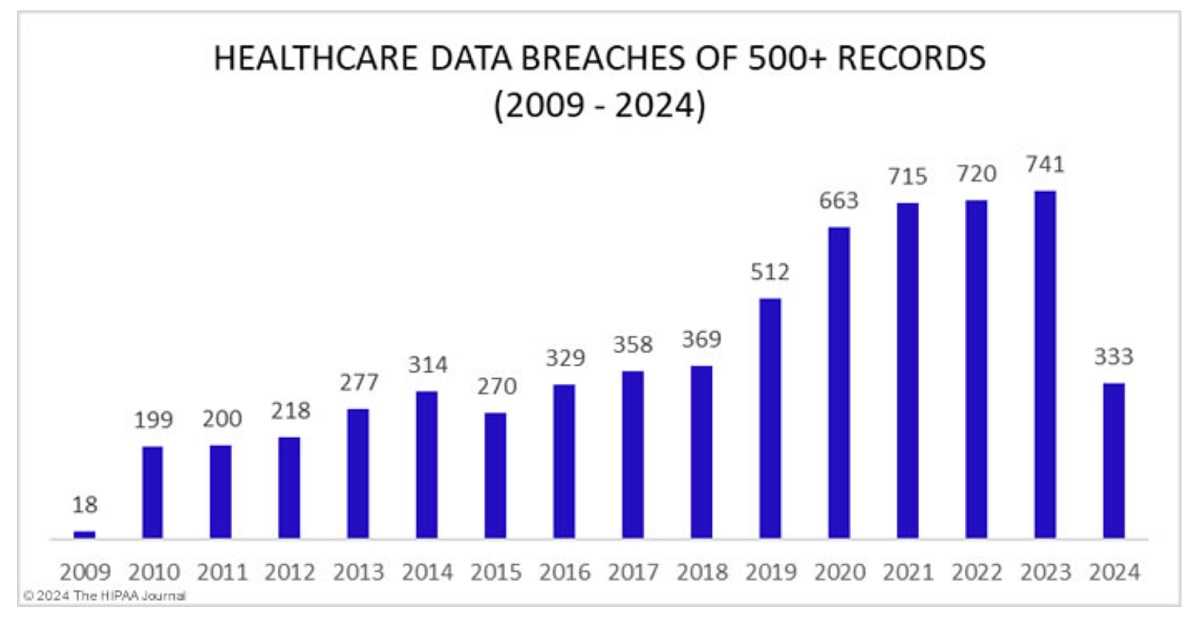
And there’s more healthcare data breach news. The Los Angeles County Department of Health Services (DHS) reported that it was the victim of a data breach that impacted thousands of patients. The organization is the second largest municipal health system in the U.S., operating clinics and hospitals throughout the southern California county. The attack occurred between February 19th and 20th of this year.
What was disclosed is the attackers were able to obtain credentials from 23 of the department’s employees. This allowed them to access the information on patients.
Per the data breach notification, a phishing email tricked DHS employees into clicking a link in the message. The employees were convinced the sender was legitimate and provided important information back to the attacker that allowed them to gain access into the network.
And this how phishing is successful. The attackers were diligent enough to make the messages seem realistic so that there was no doubt the employees would click. They may have gotten the information they used from business networking sites (such as LinkedIn or Xing), from social media posts, or by purchasing it on the dark web. There is no shortage of ways they can get it these days, which means it is important to limit what you share on the Internet.
The reason they did not alert affected patients until much beyond the occurrence of the breach was because law enforcement advised them that doing so would hinder their investigation.
While not all of the stolen information was consistent across all victims, they did say that potentially exposed information included:
- First and last name
- Date of birth
- Home address
- Phone number(s)
- E-mail address
- Medical record number
- Client identification number
- Dates of service
- Medical information (e.g., diagnosis/condition, treatment, test results, medications)
- Health plan information
DHS has started notifying affected individuals and relevant regulatory agencies as required by law. They also say that neither Social Security Numbers nor financial information was accessed.
If you received or do receive a notification that your information was part of this attack, or any healthcare-related attack, take some time to review your medical records with your healthcare providers. If you have received any type of invoice or provided any payment card details to the Los Angeles County Department of Health Services, keep an eye on your statements and contact the card issuer immediately if you notice anything that doesn’t appear to be correct. Don’t ignore the benefit statements you receive regarding your healthcare. If anything in those appears inaccurate, contact your healthcare provider to make sure it was not a billing error or your health plan to let them know.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.