

Security firm, Symantec has recently reported that there is a high likelihood that whomever was responsible for the recent global ransomware outbreak of WannaCry is affiliated with North Korea. Symantec researchers found similarities in the code for early versions of this malware, code used in 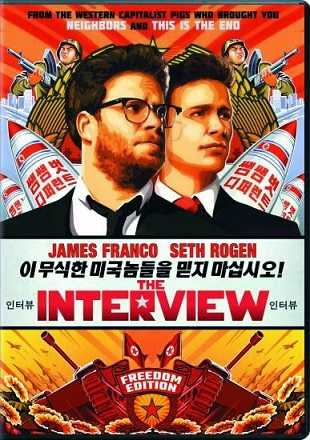 previous attacks attributed to this group, and to the malware that was used in the Sony Pictures attack in 2014 which resulted in chaos surrounding the release of a comedic movie about an attempted assassination of North Korea’s leader.
Many security companies are referring to this group as Lazarus. And while it has been suggested that Lazarus works for the North Korean government, researchers do not believe they are working for that government in the case of WannaCry. There is much speculation as to who is behind it and why, but no definitive answers have surfaced of late.
The code used that affected over 300,000 computers worldwide was part of a batch of cyber tools used by the U.S. National Security Agency and stolen by and made public by the group The Shadow Brokers several months ago. This group has been accused of having affiliation with the Russian government, but neither it nor the Russians have confirmed it.
North Korea vehemently denies any affiliation with the WannaCry outbreak and no one associated with Russia has claimed connections either.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




