

Researchers at SecureWorks have made a significant connection between the infamous hacking group Iron Twilight and the Russian Government. In a report, the security researchers stated that the group will “attempt to compromise and embarrass any organization that takes a position the 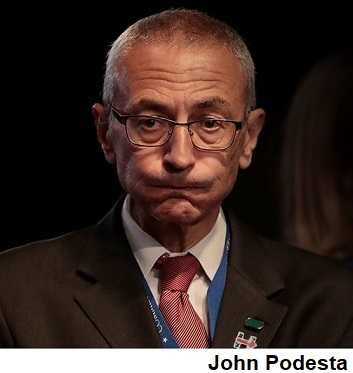 Russian government views as hostile.” Links were drawn between several recent breaches and hacking incidents including taking down a French television station and hacking into DNC computers with a simple phishing scam that fooled John Podesta.
The group, which has several aliases including Fancy Bear, APT 28, Pawn Storm, Sofacy, Strontium, and Tsar Team, has been connected to various attacks against many organizations. Generally, the majority of the attacks (41%) have been against military personnel and journalists (22%). SecureWorks wrote that the group took a departure from its original missions and became known for political targeting in 2016. In 2015, the Russian government started tasking the group with activities that went beyond the previous intelligence gathering ones. It started with such activities as sabotaging a French TV station. The damage took more than 24 hours to resolve so the station could be fully functioning.
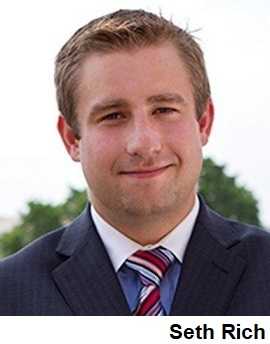 In 2016, it was linked to a breach of the Democratic National Committee servers where John Podesta’s emails were given to WikiLeaks, which then leaked them publicly. This is widely thought to be Russia’s meddling in the U.S. Presidential election. But new reports are pointing toward an inside job. There is a plenty of evidence that points to Seth Rich as the leaker with the most interesting being the exact number of files taken by Rich to be the exact number of files WikiLeaks released. Not to mention that Julian Assange has almost directly indicated that he received the emails from Rich. It is a modern day mystery that is building up a large head of steam.
Iron Twilight’s methods typically include spearphishing. Email messages are sent with malicious attachments or links that go back to custom exploit kits. They also are known to target webmail credentials by redirecting users of sites such as Gmail, but even including corporate webmail, to sites with realistic looking, but fake interfaces.
No operating system is safe either. The tricks have hit Windows, Linux, OSX and anything running on a mobile device.
There is some speculation that Iron Twilight is a part of Russia’s Main Intelligence Directorate, GRU and is deeply involved Russian covert military operations. However, no direct evidence has been discovered, yet.
For technical details on methodologies and tools the group uses, as well as more specifics, take a look at the report.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




