

The historic summit between the North Korean and U.S. leaders has come and gone and what will come of that is still TBD. But a possible reconciliation of some sort hasn’t stopped what Alien Vault researchers believe is the Lazarus group, from taking advantage of a zero-day exploit in Active X targeting a South Korean think tank that focuses on national security. This attack has been successful because that country’s government has made it a mandate to keep ActiveX enabled on most machines for reasons of its own.
It isn’t known exactly when this exploit began taking advantage of the ActiveX flaws, but it’s suspected by various experts that the initial reconnaissance scripts were deployed in January of 2017. The exploit of ActiveX may not have happened until late April of 2018. That’s a lot of time spent collecting data before “pulling the trigger” as the saying goes.
If the delivery vehicle manages to get malware onto a system, it sends a status from the victim machine indicating success. Then it profiles the machine and gathers intelligence from it. A backdoor is opened and the attackers can send commands and pretty much do what they want.
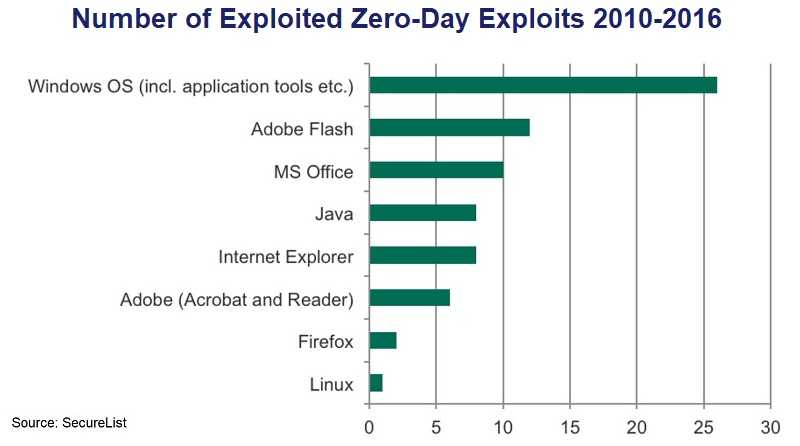
Don’t think for one moment that this group is limiting its information gathering to South Korea. It’s very likely it’s roaming around in many other countries exploiting the same ActiveX vulnerability. This is one of those moments that you take to disable ActiveX controls and all other plugins on all of your devices, if you don’t need them. If you do, be sure to update all of your software with the latest patches and updates. Microsoft has helped us all out with the Edge browser. It doesn’t even support ActiveX, which is being replaced with HTML 5 in many cases.
 If you don’t know if you need ActiveX enabled, try disabling it and see how your browsing experience is. If you don’t notice a difference, you don’t need it and can delete it completely. This is a good practice for all browser extensions and plugins. And while we’re talking about plugins that are no longer needed, go ahead and disable or delete Adobe Flash too. It’s being replaced by other options too and it is infamous for having vulnerabilities that get exploited.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




