

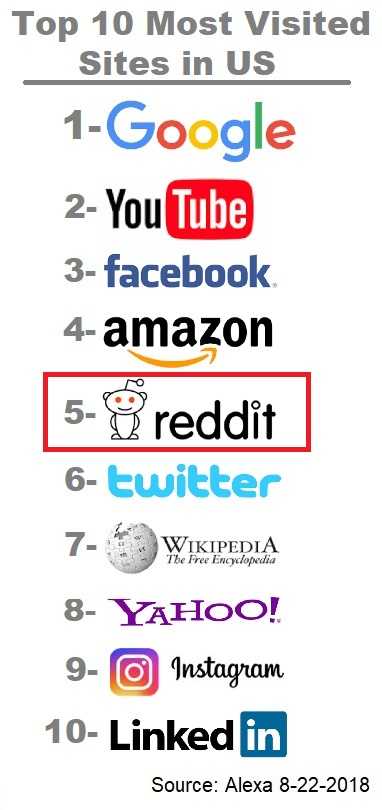
There are many places on the Internet to get news and information. One popular one is a message board that allows users to post pretty much anything they want and to do it anonymously, if they want to. However, this fifth most visited website in the U.S., according to Amazon analytics, just announced that someone accessed a large database that was tied to user accounts. This puts those that chose to remain anonymous at risk of losing that privilege.
 Reddit wrote in a post on its website that a database containing email addresses was accessed by hackers at some point prior to June 19. That’s the date the company learned of this intrusion. Anyone who created an account on the site, anonymous or otherwise, between 2005 and 2007 as well as all who were subscribed to the company newsletter between June 3rd and 17th of this were affected. The exact number of users was not listed, but it’s likely quite a large one. In any case, passwords were stolen in this case, so even if you don't think you were affected, it's a good idea to take a quick moment and change your password for Reddit.
One big concern is that because Reddit lets users post anything they want, controversial topics and participants in those conversations may now be revealed. This could harm relationships and employment, and may also lead to targeted phishing campaigns. They have email addresses and some information on users’ preferences, so it’s not a farfetched idea for someone who wants to make a buck to blackmail users with information that those users may prefer to keep secret from loved ones or employers.
It wouldn’t be the first time information gained in a data breach was used for blackmail purposes. Remember the Ashley Madison incident of a few years ago? Quick recap: Someone stole the database from the site. The site was designed to help people cheat on their significant others. They hacker threatened to reveal the behaviors if the site didn’t shut down.
 Unfortunately, deactivating your user account on Reddit isn’t going to cure the problem either. The hackers already have email addresses. They may be used to conduct phishing campaigns targeting the users. So look out for those if you used the site. If you receive email with links or attachments and you don’t know the sender or are not expecting to receive anything, don’t click them. No type of document is exempt from carrying malware these days. If you aren’t sure, verify the attachment or link with the sender by placing a quick phone call. Don’t simply reply to messages and don’t use phone numbers left in voicemail from potential scammers. Check the number using a legitimate website or other method of finding a phone number. Scamming operations actually set up what appear to be legitimate support sites with customer service staff and phone numbers that they leave in these fake messages.
In addition, use a multifactor or two-factor authentication (2FA) option on your Reddit or any other account where it's offered. This would mean that you need some other method of getting access to your account that solely a password. In this case, the users' computers that were breached in order to get to the database were using 2FA, but the hackers intercepted the one-time text code sent to their mobile phones. Yes, this can and does happen, but it's still more secure than not using any 2FA solution. Some companies have several options for 2FA. Perhaps a hardware key small enough to attach to your keychain or a fob that generates random numbers that can only be used once.
Reddit is notifying affected users by email. However, remember not to click links in these messages, as they could already be phony. Instead, change your password just to be on the safe side, but do this or check account details directly in your Reddit account.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




